Where attacks take shapeAdversaries · campaigns · exploits
CYFIRMA · the preemptive windowThreats seen and prioritized early
Your perimeter
Your organizationPrepared to act, before impact
Preemptive Cybersecurity Starts Here.
CYFIRMA connects your attack surface, threat intelligence, digital risk and third-party exposure in one view, and shows which risks attackers are likely to use, before they use them.
External Risk Is Seen Too Late, Out of Context and Without Priority
Your external environment changes continuously. Assets appear, vulnerabilities become exploitable, identities circulate, brands are impersonated and adversaries prepare infrastructure. These signals can emerge before an internal alert, but they are often separated across tools, sources and teams.
Internal controls
9Exposed cloud storage7Shadow IT asset8Dark web mention6Supplier exposure
Visibility gap
Threats form outside the enterprise boundary
Traditional security focuses inward while threat formation increasingly happens outside: unknown assets, shadow IT, exposed cloud and digital channels, third-party exposure, brand and identity abuse, and deep and dark web activity.
Attack surface
Threat intelligence
Digital risk
Third parties
Context gap
Signals stay fragmented
External signals from assets, vulnerabilities, identities, brands, suppliers, threat actors and campaigns remain fragmented across tools, feeds, teams and sources. Without correlation and attribution, intent, convergence and likely attack paths are hard to see.
Alert queue Unprioritized
7Open port on public host
9Leaked credential
4Expired certificate
8Phishing domain
6Dark web mention
5Misconfigured DNS
9New critical CVE
6Supplier breach report
7Open port on public host
9Leaked credential
4Expired certificate
8Phishing domain
6Dark web mention
5Misconfigured DNS
9New critical CVE
6Supplier breach report
Which first?
Action gap
Alert volume does not translate into decision confidence
Teams review more alerts than they can act on, without a clear view of which risk matters first or which remediation maps to the real threat.
More toolsMore dataMore alertsSeverity scores aloneNot the answer
Our view
The objective is not more alerts. It is knowing which risks to act on first, before an attack takes shape.
CYFIRMA turns what is changing outside your perimeter into early, prioritized decisions.
In practice
High Severity Is Not the Same as Attack Risk
Most teams rank findings by severity score, mention volume or supplier tier. Attackers look for what is reachable and easy to use, wherever it sits on that list.
Instead of ranking by severity alone, our platforms re-score every finding by what is exposed, exploitable and actively targeted, so your teams act first on the risks attackers are most likely to use.
Vulnerabilities
Sorted by severitySorted by attacker use Exposure Score
9.8CVSS3Remote code execution on an internal serverNot reachable from outside
9.1CVSS4Privilege escalation in a legacy appNo exploit activity seen
7.5CVSS2Outdated library on the intranetNot exposed
4.3CVSS9Information disclosure on the public login pageInternet-facing · Exploit in the wild · Linked to an active campaignActively targeted
Brand and digital risk
Sorted by volumeSorted by attacker use Exposure Score
214mentions2Brand mentions on social channelsRoutine chatter
96mentions1Product reviews quoting your nameNo malicious intent
Connected disciplinesExposure, vulnerabilities, digital risk, brand, third parties and adversary activity in one picture.
The adversary’s viewUnderstand your exposure the way an attacker sees it.
Prioritized by adversary behaviorRank vulnerabilities by how adversaries use them, not by static severity alone.
Earlier in the attack lifecycleRecognize credible risk while it is still forming.
Decisions with evidenceTurn intelligence into operational decisions, with the evidence to support them.
The Preemptive Advantage
See Risk Forming Early Enough to Change What Happens Next
Cybersecurity has spent two decades getting better at detecting attacks. The next advantage will come from seeing enough of the attack before it reaches you to change its outcome.
SeeUnderstandAnticipatePrioritizeAct
Identify meaningful external change.
Establish relevance to your environment.
Assess how credible threat activity may develop.
Focus on the risks that deserve action first.
Route evidence and recommended action through existing workflows.
See
Understand
Anticipate
Prioritize
Act
Explore by team, use case or pillar
One Intelligence Picture for Every Team, Use Case and Pillar
Executives and boards
Understand material external risk, changing threat conditions and where leadership attention is required.
Enterprise cyber-risk posture and board reporting
Crown-jewel and business exposure
Forward-looking risk outlook and executive briefings
See what attackers can reach and use. Connect external exposure and vulnerabilities with exploit evidence, likely attack paths and relevant adversary activity to determine what deserves remediation first.
Know which threats are relevant and how they may develop. Assess actors, campaigns, infrastructure and techniques against your industry, geography, technology and external exposure.
Separate routine digital noise from risks that could damage trust or enable an attack. Connect brand, identity and infrastructure exposure with adversary context and potential attack use.
See where your ecosystem could become your attack path. Connect third- and fourth-party external exposure with breach, identity, brand and adversary context to prioritize supplier risk.
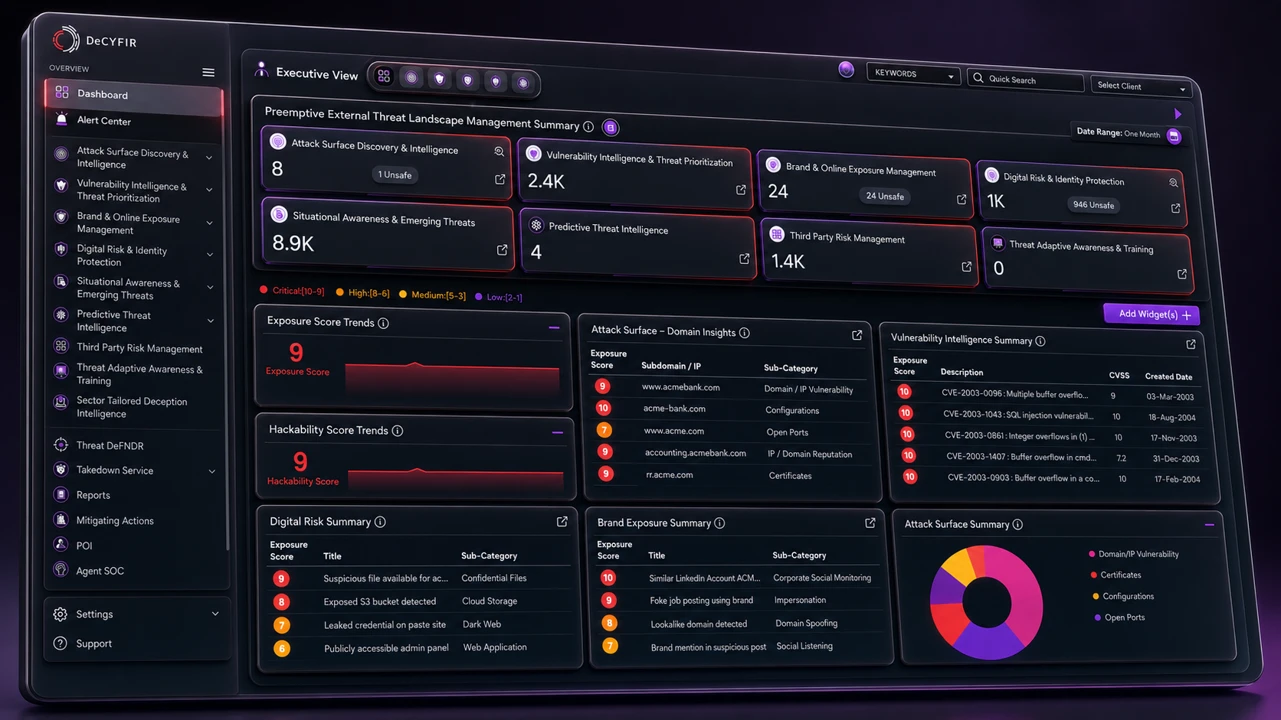
DeTCT answers: what about my digital presence is exposed and putting me at risk? DeCYFIR goes further: who is likely to exploit that exposure, how could they do it, what are they preparing, and what should I do before the attack materializes?
A decision platform for the external threat landscape. DeCYFIR shows who is likely to exploit your exposure, how they could do it and what they are preparing, so your teams can act before an attack materializes, with the evidence behind every decision.
Choose DeCYFIR if you need to
Know which threat actors and campaigns are targeting your sector
Anticipate attacks with predictive intelligence and early warning of emerging threats
Disrupt and prepare, with deception intelligence and threat-adaptive training
Continuous visibility of your digital presence. DeTCT shows what is exposed and putting you at risk, from internet-facing assets and vulnerabilities to leaked credentials, brand impersonation and supplier exposure.
Choose DeTCT if you need to
Continuously discover your external assets and vulnerabilities
Catch leaked credentials, impersonation and brand misuse early
“The best part is the correlation between all the pillars. Adding to that, alert notifications, reports, ransomware section and takedown services are a few more top mentions.”
Tell us what your organization needs to protect, and we will tailor the conversation to your external threat landscape, risk priorities and security workflows.
Your External-Risk PrioritiesStart with the exposures and threats that matter to your organization.
The Right CYFIRMA ExperienceExplore the DeCYFIR or DeTCT capabilities aligned with your needs.
A Practical Path ForwardDiscuss workflows, integrations and the next steps for your team.
This site is registered on wpml.org as a development site. Switch to a production site key to remove this banner.